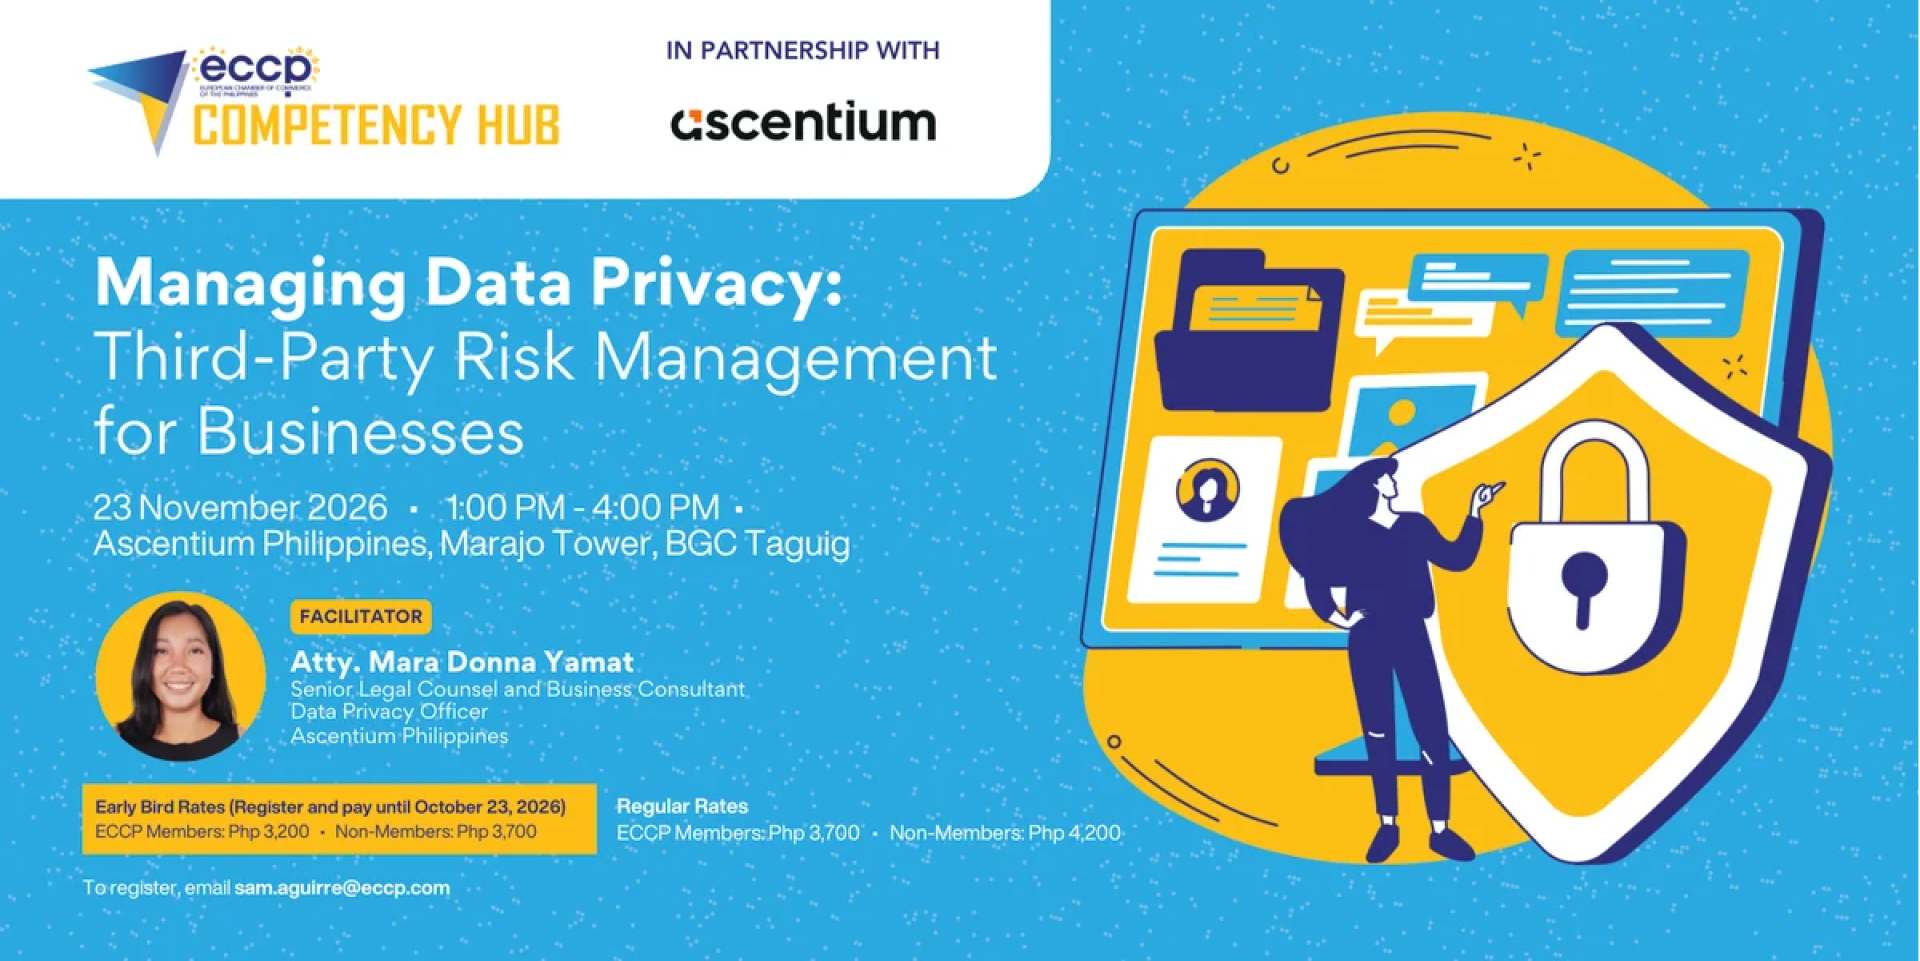
Managing Data Privacy: Third-Party Risk Management for Businesses
Program Overview
By the end of the session, participants will be able to equip with the knowledge and practical strategies to identify, assess, monitor, and mitigate data privacy risks associated with third-party vendors and business partners, while understanding relevant regulatory requirements, implementing an effective Third-Party Risk Management (TPRM) lifecycle, and addressing common gaps and challenges to strengthen data protection and regulatory compliance.
Program Outline
1. Introduction to Third-Party Risk Management
2. Regulatory and Standards Landscape
3. The Third-Party Risk Management Lifecycle
4. TPRM Gaps and Obstacles
5. Third-Party Risk Management Strategies
Target Participants
- Data Protection Officers (DPOs) and Compliance Officers
- Procurement, Vendor Management, and Legal Teams
- Information Security and IT Risk Professionals
- Business Leaders and Department Heads involved in outsourcing or vendor selection
- Invoices will be sent to the registered email address.
- PM snacks are included in the fee.
- Full payment is required at least 3 working days before the training schedule. Please send your proof of payment to trainings@eccp.com and accounting@eccp.com.
- No-shows and late cancellations will be billed at full cost. Cancellations should be made a week before or at least five working days before the event. Replacement is encouraged.
- The ECCP reserves the right to reschedule or cancel this training program. Attendees arranging travel logistics (flights and hotel) are requested to email us first to confirm if the event is pushing through.
For registration inquiries, please contact Sam Aguirre at sam.aguirre@eccp.com.